

Lab Objective:
Learn how to configure DHCP snooping on a switch.
Lab Purpose:
DHCP snooping provides protection from rogue DHCP servers on your network by creating a logical firewall between untrusted hosts and DHCP servers. We will keep this lab very simple, but you may want to create more complex labs of your own with rogue DHCP servers.
Lab Tool:
Packet Tracer
Lab Topology:
Please use the following topology to complete this lab exercise:

Lab Walkthrough:
Task 1:
Connect a router to a switch and then a PC to the switch as per the topology (all straight-through cables).
Task 2:
Configure interface G0/1 on the router with an IP address and ‘no shut’ it.
Router>en
Router#conf t
Enter configuration commands, one per line. End with CNTL/Z.
Router(config)#int g0/1
Router(config-if)#ip add 192.168.1.1 255.255.255.0
Router(config-if)#no shut
Router(config-if)#exit
Task 3:
Set up the router as a DHCP server allocating hosts from the 192.168.1.0 network. Remember to exclude the router IP address and to set the default router address.
Router(config)#ip dhcp pool 101labs
Router(dhcp-config)#network 192.168.1.0 255.255.255.0
Router(dhcp-config)#default-router 192.168.1.1
Router(dhcp-config)#exit
Router(config)#ip dhcp excluded-address 192.168.1.1
Task 4:
Configure the host to obtain IP addresses via DHCP. The IP address field should populate very quickly.

Task 5:
Enable DHCP snooping on the switch. We won’t add any trusted ports yet because we want to test that DHCP packets are blocked.
Switch>en
Switch#conf t
Enter configuration commands, one per line. End with CNTL/Z.
Switch(config)#ip dhcp snooping
Switch(config)#ip dhcp snooping vlan 1
Task 6:
Renew the IP address allocation on the PC with the ipconfig /renew command. If you wish, you can turn on simulation mode and press on the envelope to see the DCHP packet being blocked by the switch.

You will also see that the host has self-allocated an IP address due to the DHCP failure.
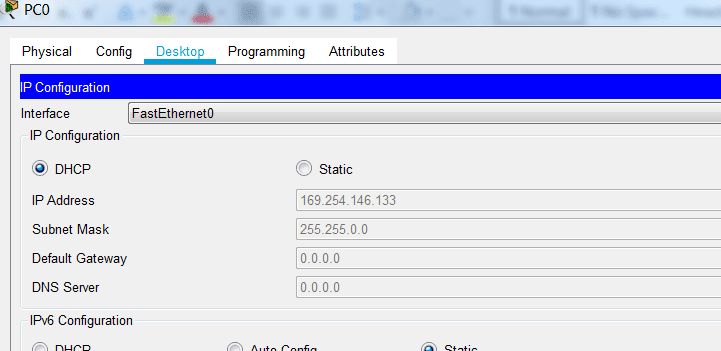
Task 7:
The router is connected to port G0/1 on the switch, so we need to set this port to trust for DHCP packets to be permitted. Packet Tracer has some limitations, so we need to add the no DHCP option-82 data insertion command to turn off a security feature.
Switch(config)#int g0/1
Switch(config-if)#ip dhcp snooping trust
Switch(config-if)#no ip dhcp snooping information option
Switch(config-if)#end
Task 8:
We will request an IP address for the host again. Feel free to use simulation mode as well.

Task 9:
Optionally, you can check the DHCP snooping binding table and compare the entry against the host MAC address.


Notes:
DHCP snooping is an important security measure you will want to implement for your LAN.
Packet Tracer seems to allow only limited information to be allocated to hosts via DHCP, so don’t worry if your DNS server or other parameters are not allocated.

